Legal Obligations for AI in Hotels
AI deployment in hotels is already subject to European and Spanish requirements on transparency, data protection, employment, consumer protection and human oversight. I propose an internal deployment licence to review every use case before it is procured, connected to operations or allowed to affect guests and employees.
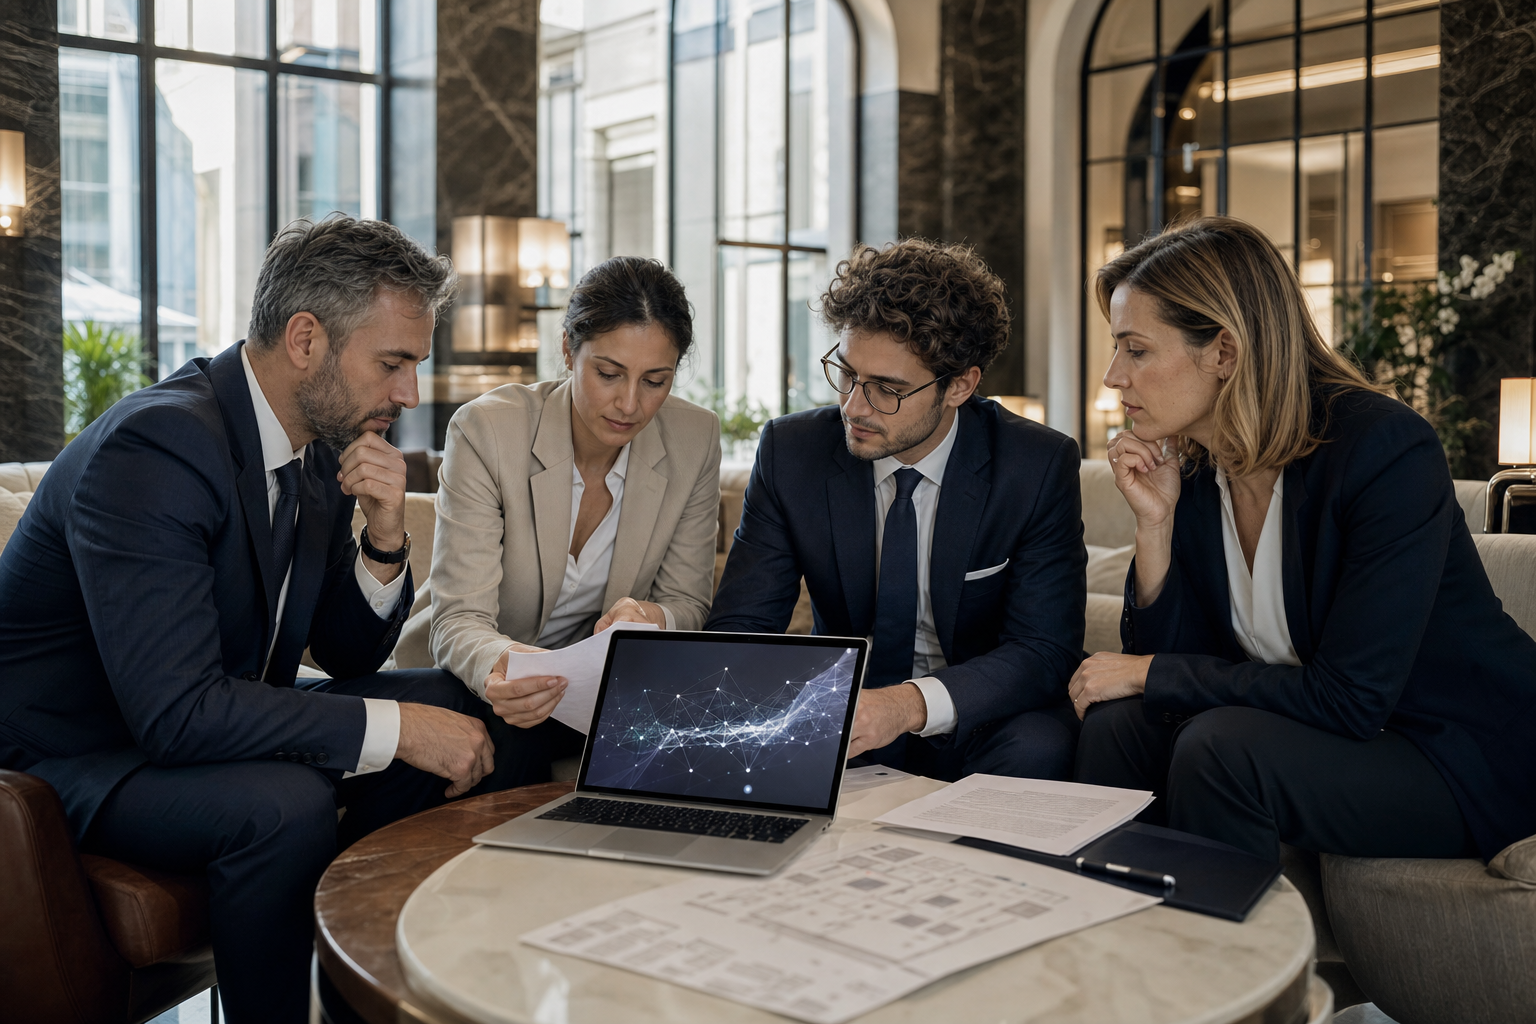
Some time ago, I took part in reviewing a tool that promised to automate part of guest service. The demonstration had convinced the sales team, the provider assured us that the solution complied with European regulations, and the projected return was attractive. Everything seemed ready to move forward until we asked a question far less eye-catching than those included in the presentation: what data would the system actually receive, what would it use it for, and who would be accountable if its recommendation harmed a guest? The meeting changed tone. We discovered that we had talked a great deal about functionality and very little about legality.
This scenario is repeated in different forms across Hospitality. One application analyses CVs, another drafts responses to reviews, a chatbot speaks with prospective guests, an engine recommends prices, a camera recognises faces, and a platform scores employee performance. Each solution arrives with a specific promise, but its legal implications rarely remain within the department that procures it. A decision initiated in Marketing may affect data protection; a productivity improvement in HR may become an employment issue; an automation in Front Office may ultimately alter the guest experience in hotels and liability towards consumers.
Keep reading without waiting for the next reset
Your free access includes 6 reads per week. Subscribe to continue now.